

Selam,
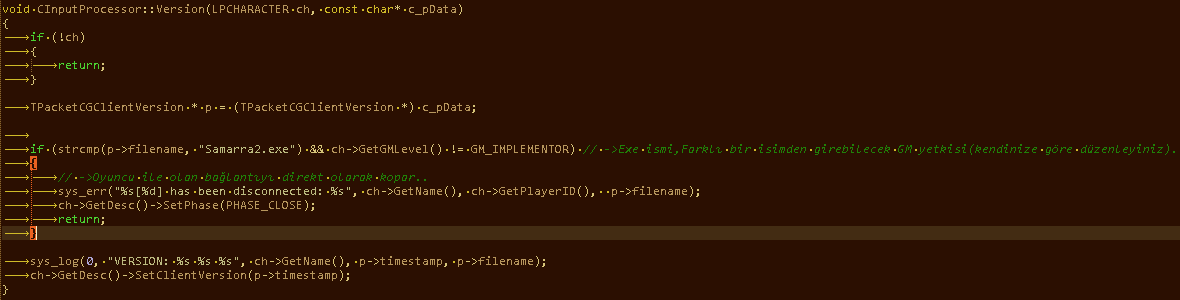
bu şekilde sağlıklı olacaktır fakat halen geliştirilebilir durumda. İyi Forumlar.
Ziyaretçiler için gizlenmiş link,görmek için üye olmalısınız!
Giriş yap veya üye ol.
Metin2 Server Geliştirme Serisi: [C++]Farklı Exe'den Girişi Engelleme!
Metin2 özel sunucularında güvenlik ve hile önleme gibi konular, sunucu sahipleri için kritik önem taşır. Bu doğrultuda, oyuncuların farklı istemci exe dosyaları üzerinden giriş yapmasını engellemek büyük bir avantaj sağlar. Bu makalede, C++ tabanlı bir Metin2 sunucu yapılandırmasında nasıl farklı exe dosyalarının kullanımını engelleyebileceğinizi detaylıca inceleyeceğiz.
Neden Farklı Exe Kullanımı Önemlidir?
Oyun istemcisinin orijinal dosyaları üzerinde değişiklik yapılmışsa, bu genellikle hile amaçlıdır. Sunucuya bağlanan oyuncuların orijinal exe üzerinden bağlanması, oyun dengelerinin korunması ve hile kullanımının önlenmesi açısından hayati bir öneme sahiptir. Özellikle PvP sistemlerinde, bu tür kontroller oyun deneyimini adil kılmak için zorunludur.
Exe Hash Kontrolü Nedir?[/COORD]
Hash kontrolü, istemcinin exe dosyasının belirli bir hash değerine sahip olup olmadığını kontrol ederek doğruluk kontrolü yapar. Orijinal exe'nin hash değeri sunucu tarafında saklanır ve oyuncu bağlandığında karşılaştırma yapılır. Eğer hash eşleşmiyorsa, oyuncu engellenir.
C++ Tarafında Uygulama Adımları
1. Öncelikle, orijinal istemci exe dosyanızın hash değerini hesaplayın. Bu işlem genellikle MD5 veya SHA256 gibi algoritmalarla yapılır.
2. Sunucu tarafında, bu hash değerini sabit olarak tanımlayın. Örneğin:
Kod:
[COLOR=green]std::string expected_hash = "a1b2c3d4e5f6...";[/COLOR]3. Oyuncu giriş yapmaya çalıştığında, gelen bağlantıdan exe hash değerini alın.
4. Alınan hash ile beklenen hash değerini karşılaştırın.
5. Eşleşmiyorsa, bağlantıyı reddedin ve kullanıcıyı bilgilendirin.
Authserver ve Gameserver Entegrasyonu
Bu kontrol genellikle authserver tarafından yapılır. Authserver, kullanıcı kimlik doğrulaması sırasında aynı zamanda exe hash kontrolünü de gerçekleştirmelidir. Eğer hash uyuşmazsa, kullanıcıya giriş izni verilmez.
Python ve GUI Entegrasyonları
Bazı durumlarda, bu hash kontrolü Python tabanlı GUI sistemlerle de entegre edilebilir. Örneğin, bir admin paneli aracılığıyla exe hash listesi yönetilebilir. Böylece yeni bir istemci sürümü çıktığında, kolayca hash güncellenebilir.
Uygulamada Dikkat Edilmesi Gerekenler
- Hash kontrolü sunucu performansını etkileyebilir. Bu nedenle optimize edilmiş algoritmalar tercih edilmelidir.
- Hash değerleri güvenli bir şekilde saklanmalıdır.
- Sistem, false positive durumlarını önlemek için iyi test edilmelidir.
Sonuç
Farklı exe dosyalarından gelen girişleri engellemek, Metin2 özel sunucuları için temel güvenlik önlemlerinden biridir. C++ tabanlı sistemlerde bu kontrolü doğru uygulamak, hem hileleri azaltır hem de oyun deneyimini daha adil hale getirir. Bu tarz teknik gelişmeler, Metin2 PvP sistemlerinde büyük avantaj sağlar.
Metin2 Server Development Series: [C++]Blocking Access from Different Executables!
In Metin2 private servers, topics such as security and cheat prevention are critical for server owners. In this context, blocking players from logging in via different client executable files provides significant advantages. In this article, we will examine in detail how you can prevent the use of different executable files within a C++ based Metin2 server configuration.
Why Is Preventing Use of Different Executables Important?
If modifications have been made to the original game client executable, it is usually for cheating purposes. Ensuring that players connect through the original executable is crucial for maintaining game balance and preventing cheating. Especially in PvP systems, such controls are essential to ensure fair gameplay.
What Is Executable Hash Check?
Hash checking verifies the authenticity of the client executable by comparing its hash value against a known one. The original executable's hash is stored on the server side and compared when a player attempts to connect. If the hash does not match, the player is blocked.
Implementation Steps in C++
1. First, calculate the hash value of your original client executable file. This is typically done using algorithms like MD5 or SHA256.
2. On the server side, define this hash value as a constant. For example:
Kod:
[COLOR=green]std::string expected_hash = "a1b2c3d4e5f6...";[/COLOR]3. When a player tries to log in, retrieve the executable hash from the connection request.
4. Compare the received hash with the expected hash value.
5. If they do not match, reject the connection and notify the user.
Authserver and Gameserver Integration
This check is usually performed by the authserver. During user authentication, the authserver also performs the executable hash check. If the hash does not match, access is denied to the user.
Python and GUI Integrations
In some cases, this hash check can be integrated with Python-based GUI systems. For instance, an admin panel could manage the list of executable hashes. This allows for easy updates when a new client version is released.
Considerations During Implementation
- Hash checking may affect server performance; thus, optimized algorithms should be preferred.
- Hash values must be stored securely.
- The system must be well-tested to avoid false positives.
Conclusion
Blocking access from different executables is a fundamental security measure for Metin2 private servers. Properly implementing this control in C++-based systems reduces cheats and makes the gaming experience more fair. Such technical improvements provide great advantages in Metin2 PvP systems.
